
One lazy driver
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




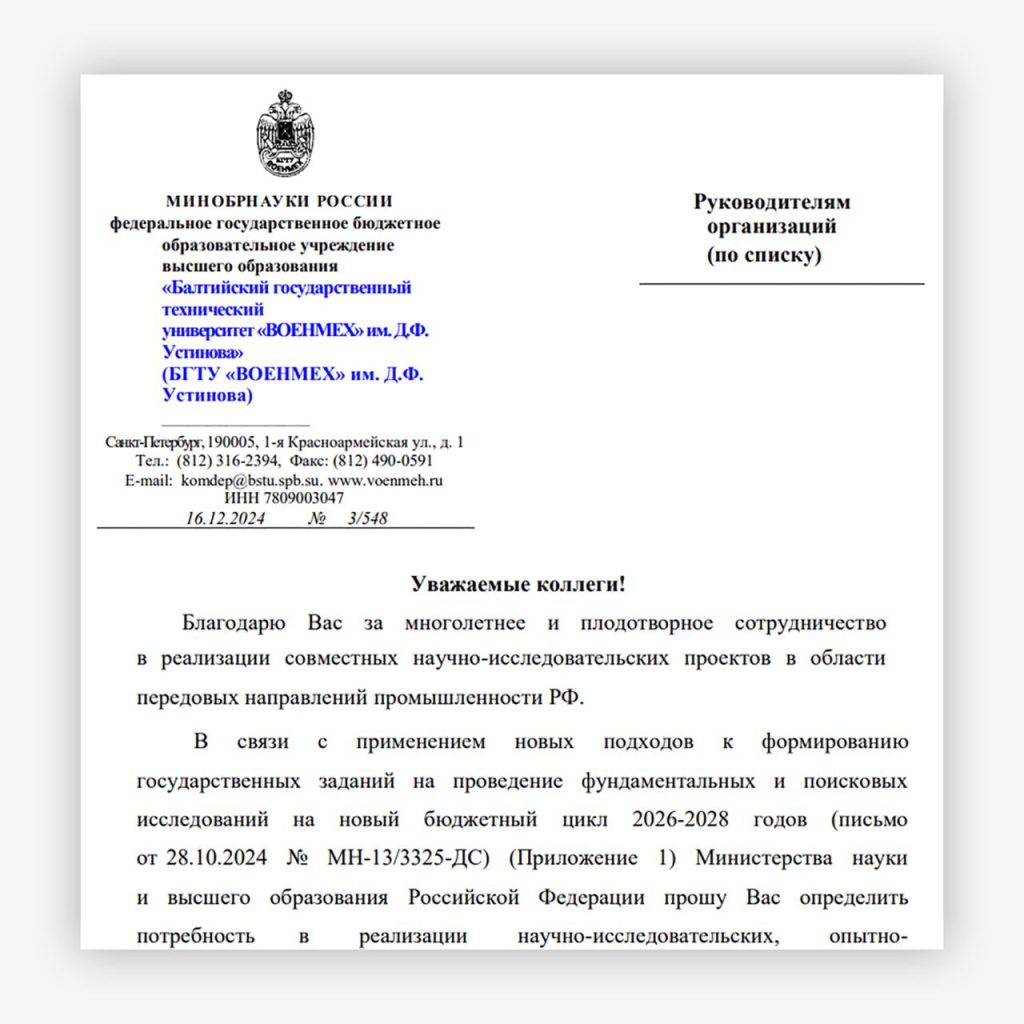
Recently, the PT ESC cyber intelligence group discovered an executable file with an “unusual” name, reinforced by a distinctive PDF file icon:
Исх 3548 о формировании государственных заданий на проведение фундаментальных и поисковых исследований БГТУ «ВОЕНМЕХ» им. Д.Ф. Устинова.exe
Code language: plaintext (plaintext)
We don’t fall for the attackers’ tricks and determine that this file is a module written in C#, and head over to dnSpy. Fortunately, we don’t observe any significant traces of obfuscation and begin to dig in. What immediately stands out are the files “embedded” in the resources:
faylyk, OneDrive, OneDriver, and Исх_по_списку_БГТУ_ВОЕНМЕХ.pdf. 1️⃣
faylyk — this is the icon that will be displayed in the system tray when the program runs;2️⃣
OneDrive — a legitimate copy of the Microsoft OneDrive program; 3️⃣
Исх_по_списку_БГТУ_ВОЕНМЕХ.pdf — a decoy, a legitimate document.🧐 But
OneDriver — that’s something unusual, something that immediately draws attention.Following the entry point, we confirm that the class
MyCustomApplicationContext is of greatest interest, in which we see manipulation of files from the resources:Исх_по_списку_БГТУ_ВОЕНМЕХ.pdf is written to the path %APPDATA%\Documents, OneDrive to the path C:\Users\Public\OneDrive.exe, and OneDriver.exe is written to the path %APPDATA%\Driver\OneDrives_v2_1.exe and added to autorun by creating an LNK file in the directory %APPDATA%\Microsoft\Windows\Start Menu\Programs\StartUp.To divert attention, the loader simultaneously opens the written decoy PDF file and the loader
OneDriver.exe.🦥
LazyOneLoader (as we named OneDriver.exe) is a loader written in the Go language. This loader is fairly trivial, but has some peculiarities.The principle of operation is quite simple: there is an encrypted buffer stored in base64 format, which during program execution is decrypted using an xor operation with the key
4c776449576c50636c5a507251.Next, the
OneDrive.exe process obtained in the previous step is launched in SUSPENDED status, in which memory is allocated using LazyDLL to communicate with Native functions (VirtualAlloc). The buffer with the decrypted shellcode is copied into this memory, and, using LazyDLL (specifically the VirtualProtect function), the memory flags are changed to Executable.And finally, using the
QueueUserAPC function, an asynchronous function object is created that begins its execution after the ResumeThread function is called on the program’s main thread.💤 Unfortunately, obtaining the final payload defined by this loader is currently not possible: the attacker has deactivated their C2 infrastructure (the domain
phpsymfony.com). But we assume that the next stages of the attack involve downloading the long-known Cobalt Strike, followed by further lateral movement.IoCs:
Исх 3548 о формировании государственных заданий на проведение фундаментальных и поисковых исследований БГТУ «ВОЕНМЕХ» им. Д.Ф. Устинова.rar
ab310ddf9267ed5d613bcc0e52c71a08
e1b88c619da8f0630e2879ab22d580ba41b36a62
14b1cd92b0a95ec76b31b0c2ec498b90d82054206f1056a58844513f89baeb55

Исх 3548 о формировании государственных заданий на проведение фундаментальных и поисковых исследований БГТУ «ВОЕНМЕХ» им. Д.Ф. Устинова.exe
fad1ddfb40a8786c1dd2b50dc9615275
34918c4d41e69dafe953fee14416f18d5e849081
ad80cbf12e5bee38a197f7bcafbe24983fdd3df6915e5a33a01f0311685e8b24

Исх\_по\_списку\_БГТУ_ВОЕНМЕХ.pdf
4c771efafb9141633ca83df3b21ad365
5f01f5f77239fb304777ce481bc3cbad40d964d4
420866ad15d5de2a6cdfab7ca317e5b20090098ad905d7cac784719f3e33360c

OneDrives_v2_1.exe
cac4db5c6ecfffe984d5d1df1bc73fdb
ef559b3e1c89fd03c427de706a1ce1fed2ae17aa
fdf0ea5d761352791545b1af0223853b31592996600c4ee5f1122e546c6165d3

phpsymfony.com
Code language: plaintext (plaintext)
#TI #malware #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…