
⚠️ PT ESC experts have detected attempts to exploit the CVE-2025-24071 vulnerability
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




⚠️ PT ESC experts have detected attempts to exploit the CVE-2025-24071 vulnerability
The vulnerability CVE-2025-24071, affecting a wide range of Windows operating systems, including server and client versions of Windows 10 and Windows 11, was identified on March 11.
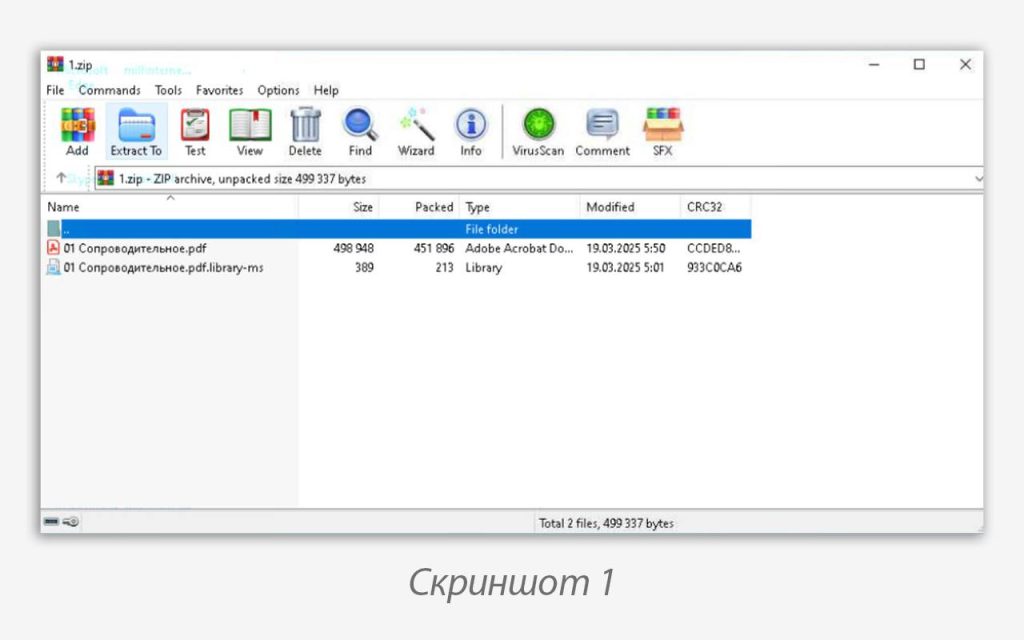
CVE-2025-24071 is related to the file handling mechanism in Windows Explorer and the indexing system — they automatically parse the .library-ms file, which is extracted when unpacking a malicious archive and contains a link to an SMB resource.
The operating system, without user interaction, initiates NTLM authentication to the attacker’s SMB server — this leads to the leakage of the NTLMv2 hash of the victim’s account, which can be used for an attack.
The description and PoC of the vulnerability were first provided by researcher 0x6rss in his blog. Experts also noted that the vulnerability can be used when saving a file with the .library-ms extension from an email.
🕵️♀️ Despite the fact that information about the vulnerability was published a couple of days ago, attackers are not sleeping: we have already detected attempts to exploit CVE-2025-24071 in organizations in Russia and the Republic of Belarus.
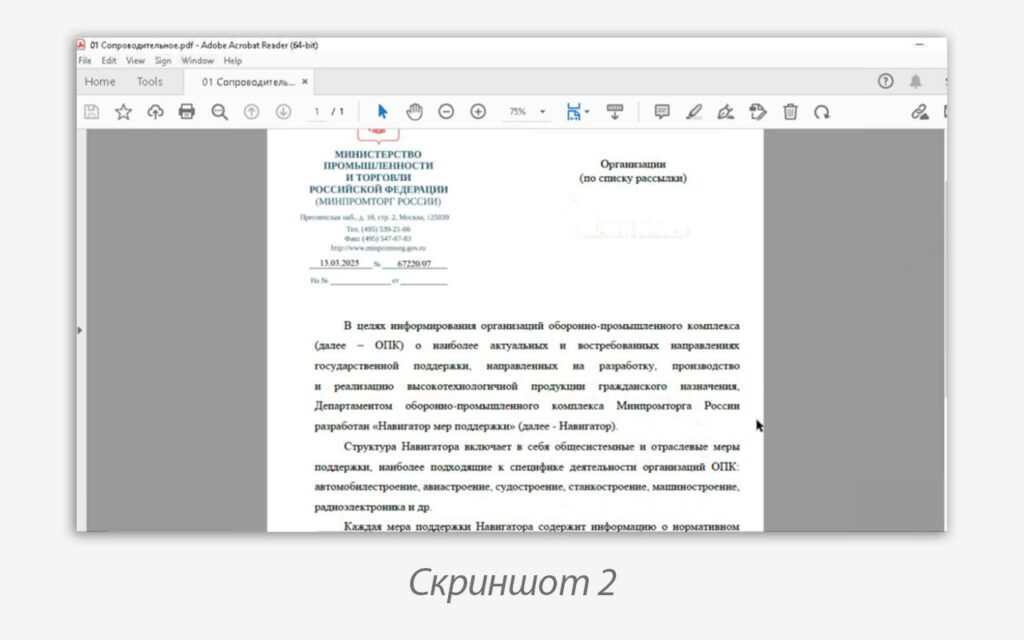
The attackers distribute archives containing a PDF document and a .library-ms file (screenshot 1). The victim unpacks the archive and launches the PDF lure (screenshot 2), while the .library-ms file automatically and unnoticed by the user sends data to the attackers’ command center.
📈 PT ESC experts predict a surge in attacks using this vulnerability. We recommend the following protection methods:
• Restrict SMB protocol connections to external servers.
• Update Windows to the latest version (install the March updates).
• Prohibit the execution of files with the .library-ms extension.
• Block the receipt of files with the .library-ms extension via email.
IoCs
Письмо Минпромторга России от 17.03.2025 № 182544_21 о направлении сведений по кадровому потенциалу предприятий 2025.pdf.library-ms
MD5: c3f9813545b7f830183369dd649bd595
SHA-1: fcadd1a24f2fa6e0f5338ff0e8d186258c79a05d
SHA-256: a4205e773eee7f33d1bb776a2f7b36da4b3955284208c015257311b8ef23f721

Письмо Минпромторга России от 17.03.2025 № 182544_21.zip
MD5: 83a60de9faed1b0a0344eda108aee44f
SHA-1: 10c02f7a3214dc166f6a8ce19c3d0a988084b3ea
SHA-256: e7897176a7d226c82af27ff525399bd0c7d7b73fdfffac8d2d56b8707637aa99

01 Сопроводительное.pdf.library-ms
MD5: 74e2f206e99040868b60eef04781de8a
SHA-1: f27ecc7ec9c6425a41a3cbfa8bf74f24c32c6488
SHA-256: 8a3728ebdb64e69347c14356b250eb0720801ce367acd1b53510a8dea16f7001

01 Сопроводительное.zip
MD5: 78cd8d4481713fbd4beb790a127bd793
SHA-1: 595b68aaad8a705e78125735cdb7136b6f17b077
SHA-256: 07f6d81b5e3fba23f5de34038424ebec4710cbc16959de4389ceb7855e69bac2

spisoc.library-ms
MD5: 9bab71704cefac935546e09d12dfd2c1
SHA-1: 922c6ee612bd22a85cd1e84f50e18d21656c3f3d
SHA-256: cb9810b6492aad667554958332a3518aeed8d356dcd03b43e4116cd92c938d0f

154.205.148.56
38.60.247.250
94.250.249.129
#win #news #cve #detect #ioc
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…