
Attackers compromised dozens of NPM packages with ~2 billion downloads
More in Supply chain
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- Did someone say sandbox?
Someone said sandbox? 👀 Once again we're watching threat actors conduct unethical research. Given: Security researcher…
- Hello! The Supply Chain Security team is here
Hello! The Supply Chain Security group is here 🩷 We scan open source in real time…
- The attacker publishes .bash_history view without registration and SMS
Attacker publishes .bash_history watch without registration and SMS 😱 The Supply Chain Security team sent a…
Attackers compromised dozens of NPM packages with ~2 billion downloads 🐾
What happened
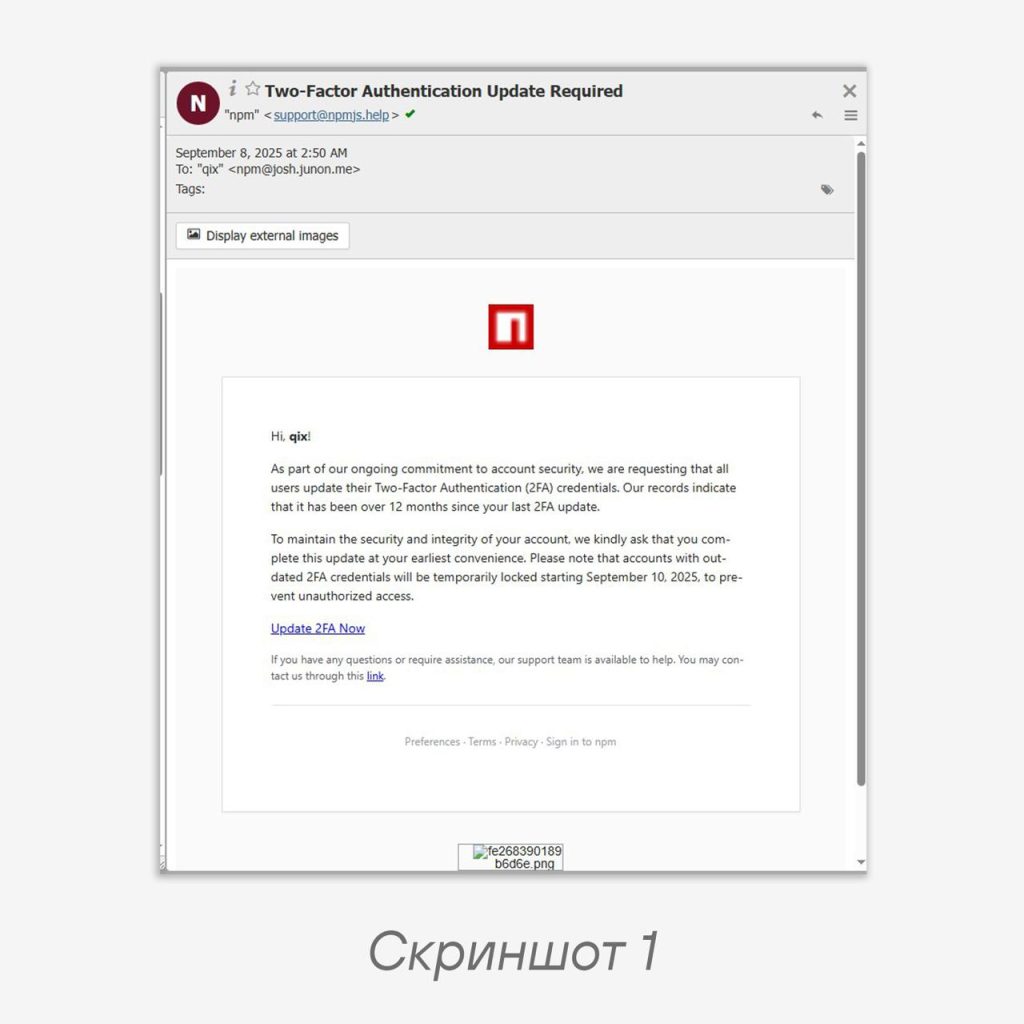
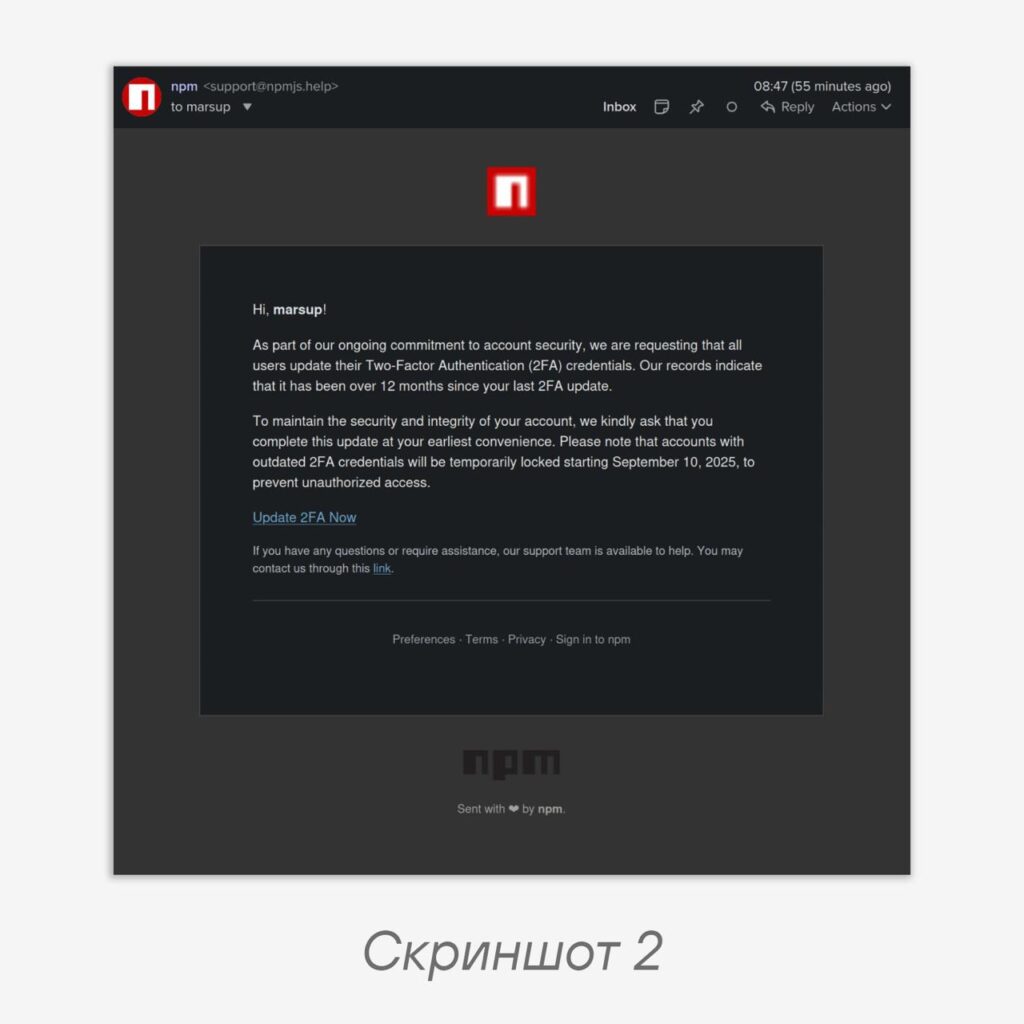
As part of a phishing campaign, maintainer Josh "Qix" Junon was compromised.
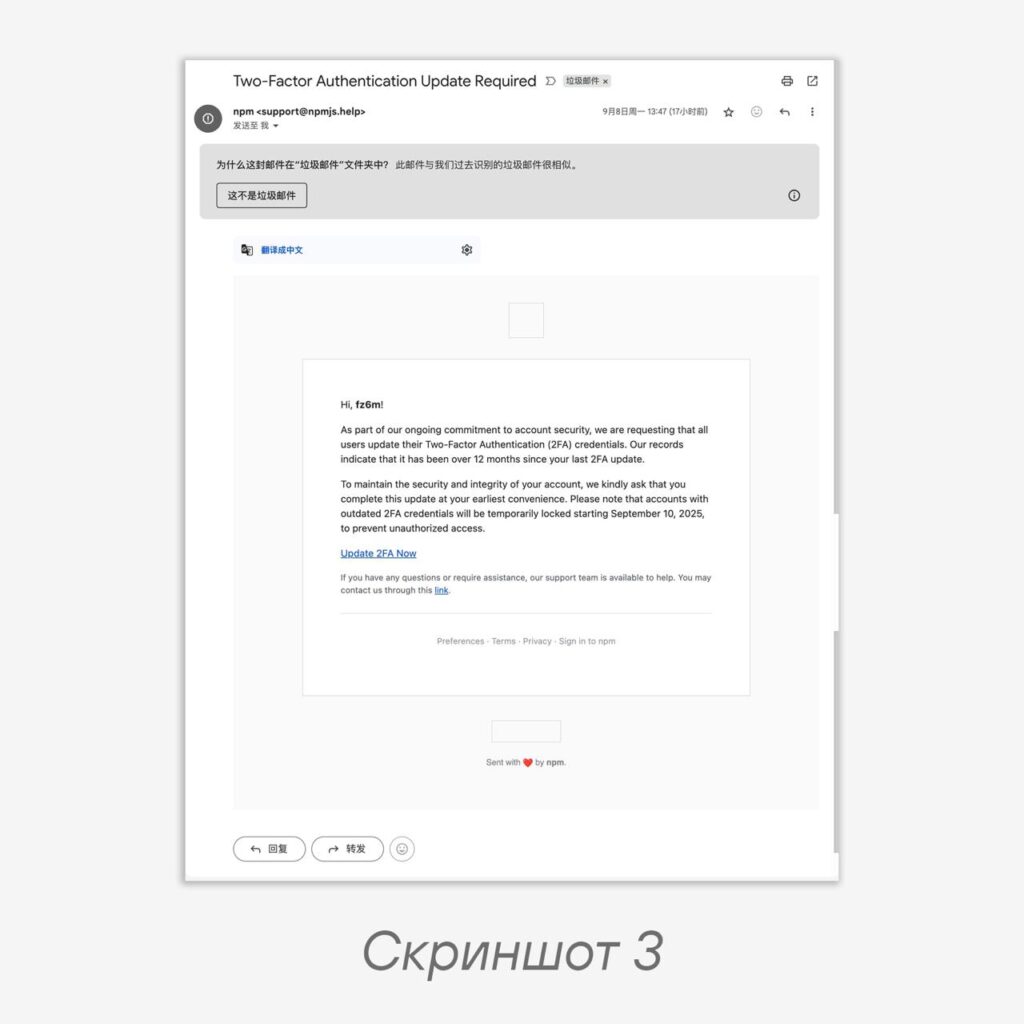
He and several other developers received an email asking them to update their second factor, as it had been 12+ months since the last change (screenshots 1, 2, 3). The email came from an address imitating the official one (support@npmjs.help). 🐱
Qix is a maintainer of major projects in the NPM ecosystem, including:
🟢chalk (882 forks and 22.7k stars on GitHub, 313 million downloads on NPM in the last week);
🟢debug (957 forks, 11.3k stars, 372 million downloads);
🟢strip-ansi (272 million downloads);
🟢wrap-ansi (206 million downloads);
🟢has-flag (200 million downloads).
Check that the attack didn’t affect you
Arm yourself with osv-scanner. Information about the malicious packages is already in the osv.dev database.
You can use a community script or check the packages listed there yourself (npm ls, yarn why, pnpm why).
Recommendations for maintainers
1. If you have to log in via links from emails — verify the URL. Remember that you are a tempting target for attackers.
2. Use a second factor. Even if an attacker can lure it out with a phishing login page, they will have to obtain it again and again if you have 2FA set to Authorization and writes mode (confirmation of all sensitive actions, including publishing a new package version, the mode is enabled by default).
3. Familiarize yourself with OIDC/"trusted publishing" practices — this way you make the target harder for an attacker, since they will have to compromise a public CI/repository to carry out the attack.
Recommendations for developers
1. Pin your dependencies. Don’t let the package manager simply pull the latest release of the dependencies you use.
2. Add dependency auditing (osv-scanner can work as a starting point) — this way you can learn about problems at the dependency scanning stage, rather than from the news.
Recommendations for AppSec
You already know all this without us:
1. Set up an internal proxy with quarantine support for internal projects.
2. Make sure your developers go through the internal proxy rather than pulling packages from global repositories. 🐱
Stay safe 👍
#npm #supplychain #appsec
@ptescalator
More from global_author
- This is Siemens...
Recently, our colleagues from the Positive Industrial Expertise Center discovered a curious Windows sample on MalwareBazaar.…
- Anti-antivirus
Recently, we came across an APK with an intriguing and trust-inspiring name: «Антивирус ФСБ.apk». After installing…
- .exe .docm .xlsm
.exe .docm .xlsm Malicious files with these extensions are most often found in corporate network traffic.…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- ::%16777216 — so what exactly are you?
::%16777216 — so what exactly are you? It is known that during attacks, adversaries can use…




More in Supply chain
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- Chaos, shock, private keys from a not-so-private GitLab 💻
Over the past couple of months, the attacker has been distributing trojans from several npm accounts:…
- Did someone say sandbox?
Someone said sandbox? 👀 Once again we're watching threat actors conduct unethical research. Given: Security researcher…
- Hello! The Supply Chain Security team is here
Hello! The Supply Chain Security group is here 🩷 We scan open source in real time…
- The attacker publishes .bash_history view without registration and SMS
Attacker publishes .bash_history watch without registration and SMS 😱 The Supply Chain Security team sent a…